When staff use the same phone for work email, customer messages and quick admin tasks, it’s easy for a single ‘allow access’ tap to give an app more reach into company data than anyone intended.
The risk often builds quietly through everyday behaviour: installing a helpful scanner for a one-off job, switching on a new keyboard, or agreeing to ‘always allow’ permissions just to stop pop-ups and get back to work.
Tas Skoudros, Founder & Managing Director of StackTrack in Bournemouth, UK, works with growing businesses to improve technology operations, security and day-to-day reliability, including the practical controls that keep staff productive without creating new risk through unmanaged devices and apps.
“Companies are often a lot more exposed through staff phones than they realise because everyday apps ask for broad permissions that people accept just to get on with their work. Over time, that creates a hidden layer of access to company emails, files, contacts, and accounts that most businesses never properly review. The real issue is not the apps themselves, it’s the lack of control over what they can see and do once they are installed on devices that are being used for work every single day.”
Privileged permissions treated like normal app requests
When a staff member installs a third-party keyboard to type faster, that app can potentially observe everything they type, including passwords, multi-factor authentication (MFA) codes, internal messages and customer details.
The biggest mobile security risk often comes from permissions that look harmless during setup but actually grant deep access to the device. These include VPN profiles, accessibility services, custom keyboards, screen recording, clipboard access, device administration and screen overlay permissions.
These are not just ‘preferences’; they’re powerful system-level capabilities that can significantly increase the damage if an app is compromised or behaves badly. The problem is that they’re often granted quickly, then left in place because nothing immediately breaks or looks unusual.
The low-hassle lockdown is to treat these permissions as restricted, not optional add-ons. On any phone that can access company email, files or systems, unapproved third-party keyboards, screen recorders, VPN profiles, accessibility services and device admin apps should be blocked by default.
Only trusted tools should be allowed, such as mobile device management (MDM) software, approved security apps, password managers, and properly vetted accessibility solutions where there’s a genuine need. This keeps high-risk access points tightly controlled without affecting normal day-to-day use.
Top tip: On managed phones, set a rule that only approved keyboards can be enabled, so staff can’t switch to a ‘typing assistant’ during a busy day and forget it’s still active afterwards.
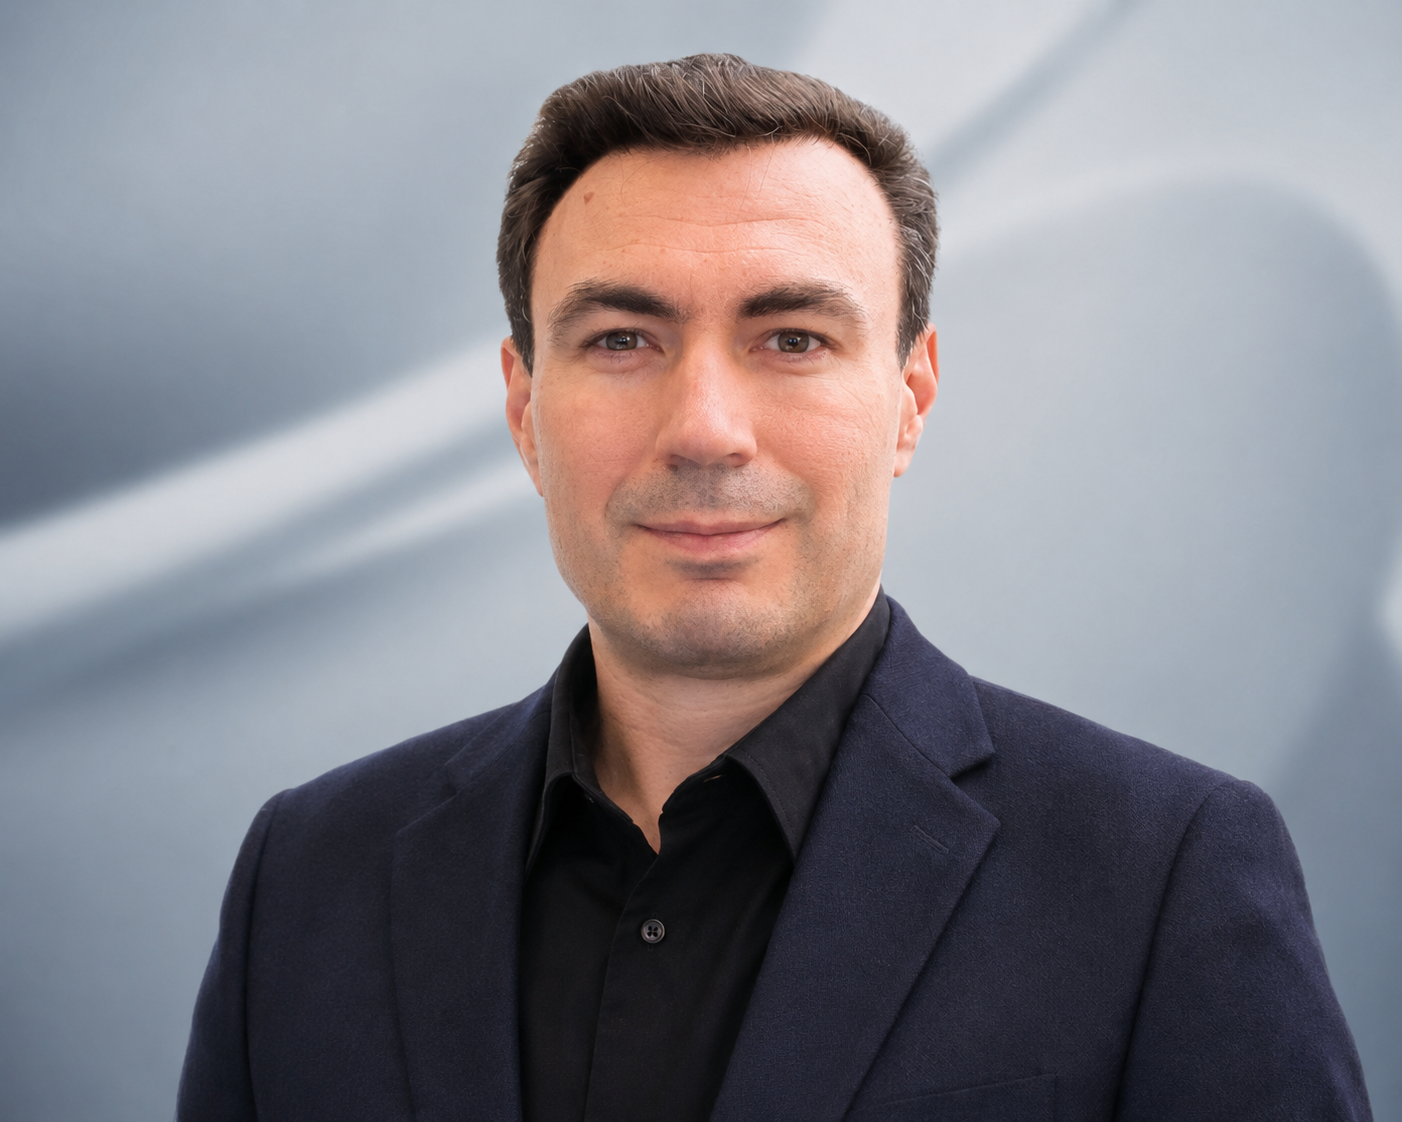
Tas Skoudros, Founder & Managing Director of StackTrack in Bournemouth, UK
Personal apps and backups becoming hidden routes into work data
When work email sits on the same device profile as personal cloud backups, messaging apps and browser sessions, company data can end up in places the business can’t see or control.
The main issue isn’t simply bring your own device (BYOD), it’s the blending of work and personal accounts, shared storage, contact syncing and unmanaged backups that quietly copy work content into personal systems.
On Android, a managed work profile keeps business apps and data separate from personal apps, which reduces the risk of personal apps accessing or duplicating work files.
On iOS, managed accounts, managed apps, and MDM controls help prevent work data from being copied into unmanaged apps without needing access to personal photos, messages or browsing history.
The goal is separation, not surveillance, so staff can still use their own phones without turning every personal app into a potential data pathway.
Top tip: Make ‘work profile required for company email’ the default for BYOD, so work mail can’t be added to a personal inbox that also syncs into personal backups.
Unmanaged convenience apps becoming mobile shadow IT
When someone needs to scan a contract, share a file or take quick notes, they often download whichever free app is easiest to find in the app store.
The issue is that these convenience apps, such as PDF scanners, note-taking tools, file transfer apps, personal cloud storage, messaging apps, QR scanners and AI tools, can ingest documents, images, contacts, calendar entries, screenshots and customer data into services the business doesn’t control.
In practice, a ‘quick scan’ might end up stored in a personal cloud account, or meeting notes containing customer information could sync to an account that stays active long after someone leaves the company. This creates invisible data movement that’s hard to track and even harder to recover.
The simplest fix is to provide approved tools for the tasks people actually need to do, such as scanning, file sharing, messaging and note-taking.
When staff already have trusted options, they’re far less likely to fall back on risky shortcuts during busy moments. It also gives the business a clear record of where data is stored and shared, which matters when customers ask what happened to their information.
Top tip: Keep a short approved apps list in a visible internal space like a company chat channel or intranet, and include one approved scanner and one approved file-sharing tool so staff don’t have to improvise under pressure.
‘Always allow’ permissions becoming the accidental default across the workforce
When apps request access to location, microphone, Bluetooth, contacts, calendar, photos, camera or files, many users accept all permissions just to get rid of the prompts.
Over time, this means apps end up with far broader access than they actually need to function. ‘Always allow’ location access, full photo library access, microphone access, Bluetooth access and contact syncing often benefit the app more than the user, especially on devices that also contain work messages, customer details, screenshots and attachments.
Even legitimate apps can become a risk if they’re granted unnecessary background access across a large number of devices.
The fix tightening defaults and making permission choices intentional. Businesses should define what level of access is actually required by job role and push ‘while using the app’ or limited access settings wherever possible.
Continuous or background access should only be allowed when there’s a clear operational need, not just because the app asks for it. Clear guidance also helps staff make better decisions in the moment instead of guessing.
Top tip: During the setup of any work-related app, quickly check permissions and make it standard that contacts, photos and microphone access must be justified before being allowed.
Weak device basics turning a lost phone into a breach
When a phone is lost in a taxi, left on a table or stolen from a bag, the real risk depends on what’s already accessible on it.
An unlocked or poorly secured device that contains work email, messaging apps, cached files, browser sessions and authentication prompts can quickly turn a simple loss into a serious data incident.
Attackers don’t need much time if access is already open or weakly protected, especially when phones are used for approvals, logins or file access.
The basics matter most here: supported operating systems, automatic updates, strong screen locks, biometrics backed by a proper PIN, full device encryption, remote wipe capability and the ability to revoke access instantly when a device is lost or when someone leaves the organisation.
These controls reduce how quickly a lost device turns into a wider breach and limit how far access can spread.
Top tip: Require any device used for company email to have a strong PIN as well as biometrics, and ensure remote wipe is enabled so a lost phone can be shut down as soon as it’s reported.